MOTOSHARE ๐Ÿš—๐Ÿ๏ธ
Turning Idle Vehicles into Shared Rides & Earnings

From Idle to Income. From Parked to Purpose.
Earn by Sharing, Ride by Renting.
Where Owners Earn, Riders Move.
Owners Earn. Riders Move. Motoshare Connects.

With Motoshare, every parked vehicle finds a purpose. Owners earn. Renters ride.
๐Ÿš€ Everyone wins.

Start Your Journey with Motoshare

error “Authorization grant type is not supported by the authentication server”

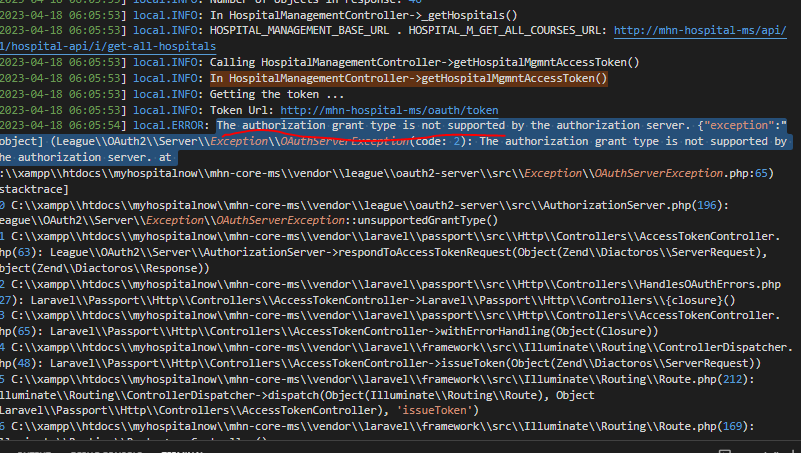
The error message “Authorization grant type is not supported by the authentication server” typically occurs when the authentication server does not recognize or support the specific grant type requested during the OAuth or OpenID Connect (OIDC) authentication process.

In my case:

This error through in my laravel.log
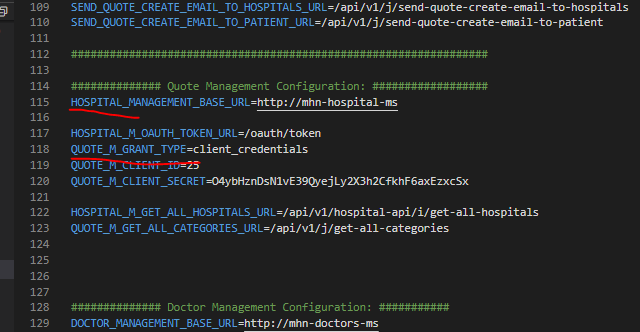
In .env file by mistake I forget to write my QUOTE_M_GRANT_TYPE

AFTER writing this then this problem will resolve
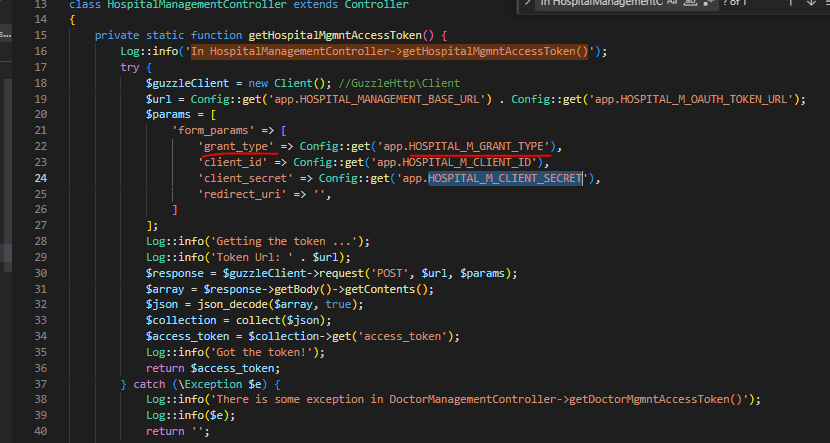
NOW, Here i define in my controller function HOSPITAL_M_GRANT_TYPE
Here are a few possible reasons and steps you can take to troubleshoot this issue:

Verify the supported grant types: Check the documentation or specifications of the authentication server you are using to confirm which grant types are supported. OAuth 2.0 defines several grant types, such as authorization code, implicit, client credentials, and resource owner password credentials. OIDC adds an additional grant type called hybrid. Ensure that you are using a supported grant type according to the server’s capabilities.

Check the request parameters: Review the request parameters you are sending to the authentication server. Verify that you are including the correct grant type parameter (grant_type) and its value. Make sure it matches one of the supported grant types of the authentication server.

Validate the client credentials: Ensure that you are providing the correct client credentials (client ID and client secret) when making the authentication request. The authentication server may reject the request if the client credentials are invalid or not properly configured.

Verify the endpoint URLs: Double-check the endpoint URLs you are using for authentication. Ensure that the authorization endpoint and token endpoint URLs are correct and correspond to the authentication server’s configuration.

Related Posts

Bihar Tourism: The Ultimate Guide to Must-Visit Places, Rich Heritage & Local Life

Few destinations across the subcontinent carry the historical weight of Bihar. This is the land where wandering ascetics reshaped world philosophy, ancient scholars debated mathematics in multi-story…

Read More

Insider Guide to Upcoming Shows, Tickets & Things to Do

Beyond the iconic domes of the old city and late-night kebabs in Hazratganj, a dynamic, modern energy fuels the streets of Awadh. Today, you are just as…

Read More

Finding the Best Knee Replacement Hospitals in India: A Patient-First Guide to Choosing Care

When severe joint stiffness begins dictating your daily scheduleโ€”turning a routine walk, climbing a flight of stairs, or getting up from the dining chair into an ordealโ€”discussions…

Read More

Ultimate Guide to Kolkata Events: Tickets, Top Activities & What’s On

There is a distinct rhythm to life in this city, where centuries-old heritage effortlessly blends with a modern, buzzing social calendar. From intimate acoustic gigs tucked away…

Read More

The Indian Travelerโ€™s Blueprint: Visas, Documents, and Pathways to Moving Abroad

Anyone holding an Indian passport knows that booking a flight ticket is rarely the hard part of going abroadโ€”getting the visa stamped is where the real work…

Read More

Modern DevOps Training in China: Practical Skills, Certifications, and Engineering Pathways

Shipping software reliably at scale has become a primary operational challenge for engineering organizations. Outdated handoffs between software developers and infrastructure administrators introduce delays, manual misconfigurations, and…

Read More
0 0 votes
Article Rating
Subscribe
Notify of
guest
0 Comments
Oldest
Newest Most Voted
Inline Feedbacks
View all comments
0
Would love your thoughts, please comment.x
()
x